TSA Pipeline Security Directives in 2026: What They Require, and Why They Matter Even If You’re Not Covered
Three professionals reviewing pipeline network data on laptop with refinery in background, illustrating TSA pipeline security directive requirements

In May 2021, Colonial Pipeline shut down the line that carries roughly 45 percent of the East Coast’s fuel, and investigators found no sign the ransomware behind it ever reached the systems that run the pipeline. DarkSide hit the business network. Colonial stopped the flow anyway because nobody could prove where the damage ended, and … Read more
Switching Healthcare IT Providers: When to Leave, What to Weigh, and What Success Looks Like

Two professionals reviewing an IT transition guide at a desk, illustrating how to evaluate switching healthcare IT providers

Should You Switch Healthcare IT Providers? Switching healthcare IT providers means moving your managed IT, security, and HIPAA business associate obligations from one MSP to another without losing clinical uptime, control of PHI, or compliance evidence. It makes sense when your MSP keeps missing clinical-down SLAs or can’t produce your HIPAA documentation, and a documented … Read more

What Actually Happens When a Senior Living Community Gets Hit by Ransomware

Healthcare IT and security professionals responding to a cybersecurity incident in a senior living community while reviewing a security alert on a workstation.

The medication cart doesn’t log in. That’s usually the first sign anyone notices, hours after the actual breach began. A senior living ransomware attack is a targeted breach in which malicious software encrypts a community’s clinical and administrative systems, cutting off access to electronic health records, medication administration records, and resident data until a ransom is … Read more

A Plain-English Guide to CMMC, NIST, and DFARS for Manufacturers

Manufacturing operations manager reviewing printed technical drawings at a workbench inside a modern precision manufacturing facility with CNC machines in the background.

Your prime contractor’s last email had the word CMMC in the subject line, and you nodded along like you knew exactly what that meant. You didn’t, and neither did the plant manager two lines down from you who forwarded it hoping someone else would open it first. Nobody hands you a glossary. Everyone just assumes you already know … Read more

IT Budget Benchmarks for Financial Services Firms: What to Spend and Where

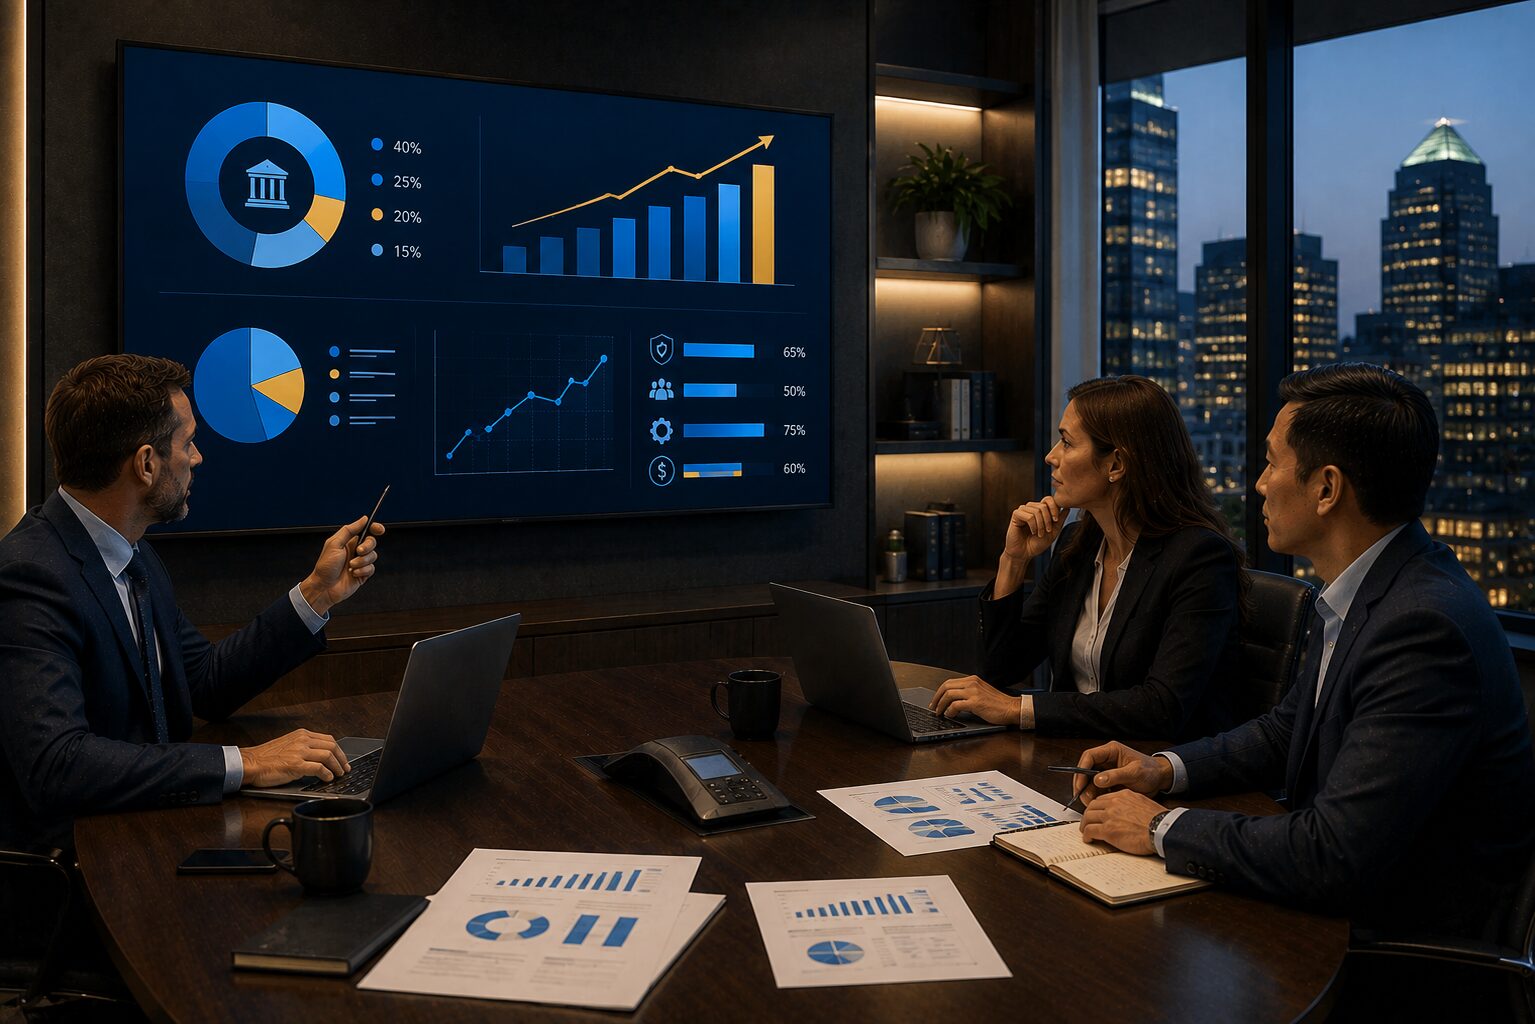
Executives reviewing IT spending charts and benchmarks on screen, illustrating IT budget benchmarks for financial services firms

The IT budget benchmark most financial institutions use to plan next year’s spending comes straight from JPMorgan Chase’s 10-K. If your institution has 400 employees instead of 300,000, that benchmark isn’t just unhelpful. It’s actively steering you wrong. An IT budget benchmark for financial services is the share of revenue, generally 7 to 10 percent, … Read more

Is Your Dealership’s IT Company Costing You Deals? Signs It’s Time for a Change

Dealership sales manager looking toward an unresponsive computer while a customer waits to sign paperwork at a desk inside a modern automotive showroom.

The desk is buttoned up. The customer’s ready to sign. Then the e-contracting system freezes. Or it’s mid-Saturday, the WiFi drops, and three salespeople are suddenly pitching vehicles from memory instead of pulling up trade values. You call your IT company. You wait. The customer doesn’t. That’s not a technology problem. That’s a vendor problem wearing a technology costume. Signs to switch your dealership IT … Read more

Cybersecurity & Compliance for Behavioral Health Practices: What 42 CFR Part 2 Means for Your IT

Woman working on laptop with global data security shield displayed on screen, illustrating cybersecurity compliance for behavioral health practices

42 CFR Part 2 compliance IT means configuring your network, EHR, and vendor stack to meet the federal confidentiality rule for substance use disorder treatment records, a rule stricter than HIPAA alone. In practice, that means segmenting SUD counseling notes from standard clinical records inside your EHR, building audit logs detailed enough to produce a disclosure accounting … Read more

Government IT Solutions: What Municipalities & Public Agencies Need in 2026

Officials meeting in government conference room with IT services icon dashboard, illustrating government IT solutions for municipalities and public agencies

Somewhere in your building sits a server old enough to vote, running software nobody’s supported in years, and a budget that won’t touch replacing it until something breaks first. That’s not a hypothetical. It’s the starting position for most municipal and public agency IT teams heading into 2026.  Government IT services means the managed technology support, cybersecurity, and compliance work that helps cities, townships, counties, and … Read more

Vendor Consolidation for Multi-Location Behavioral Health Groups: A COO’s Guide to IT Oversight

Executive presenting multi-location facility dashboard to team, illustrating vendor consolidation and IT oversight for behavioral health groups

Vendor consolidation for a behavioral health practice means reducing and standardizing EHR, network, and security vendors across locations so the organization has one consistent security and compliance posture instead of a different one at every site. It’s a risk reduction strategy first and a cost-cutting exercise second, since inconsistent vendor oversight creates gaps under both … Read more