Ask three security vendors to explain MDR vs EDR and you’ll get three answers, each ending with their own product. That isn’t a conspiracy. It’s marketing, and it leaves IT directors sorting out acronyms that sound interchangeable and aren’t.
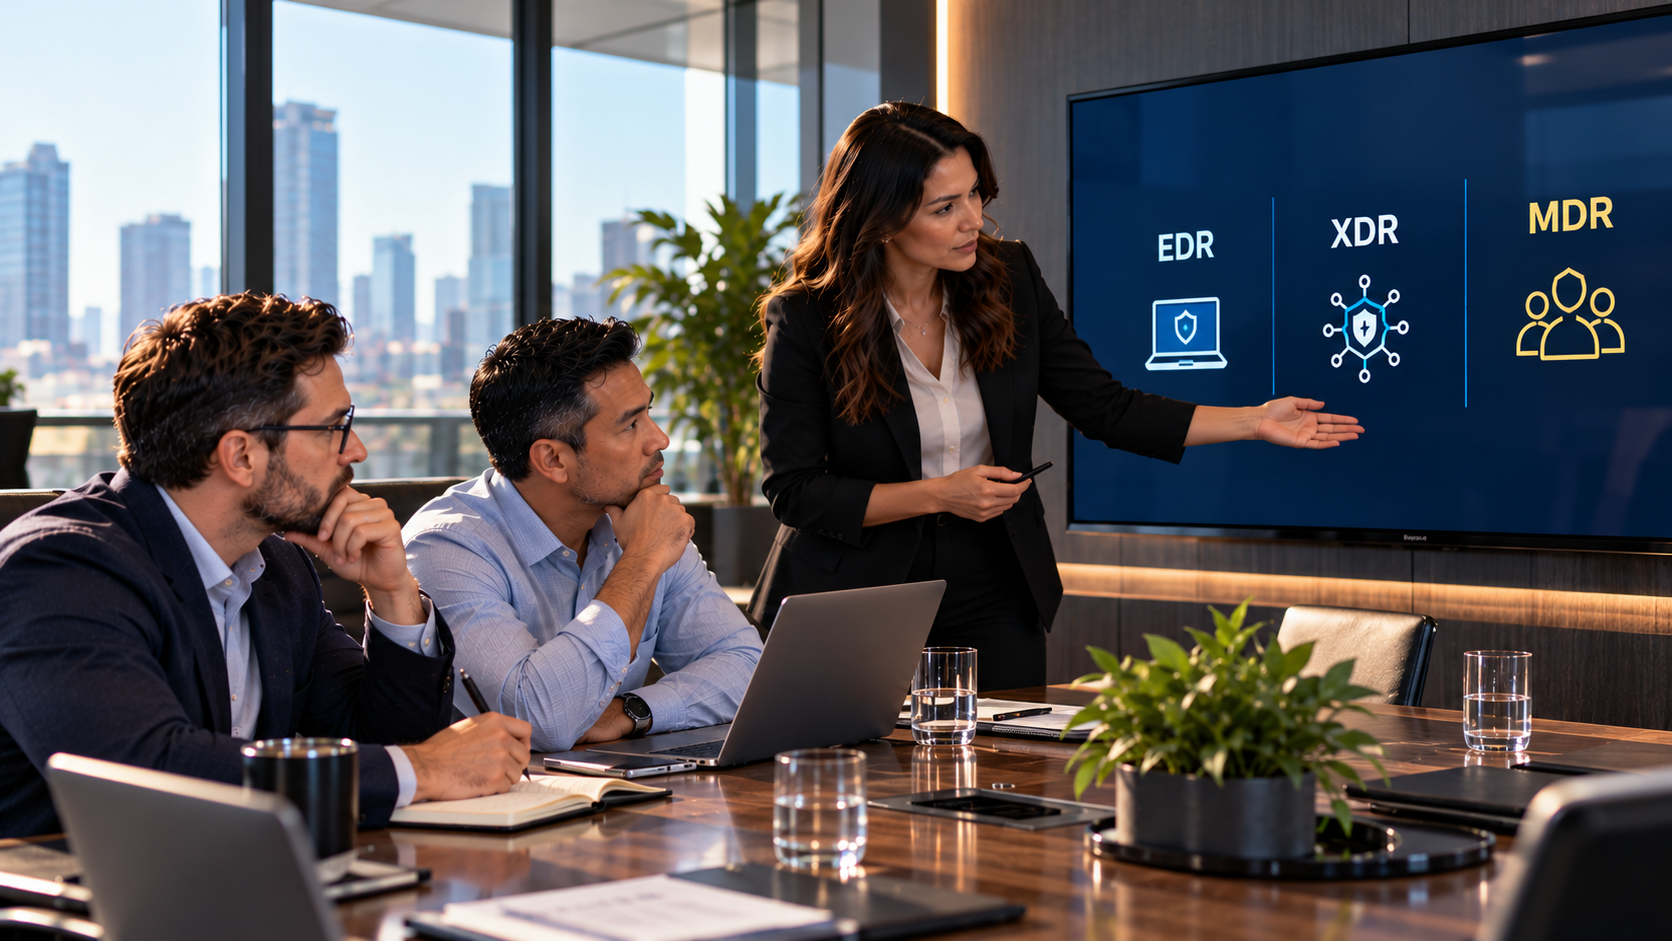
MDR vs EDR is a choice between a service and a tool. EDR (endpoint detection and response) is software that records and flags suspicious activity on laptops, desktops and servers. MDR (managed detection and response) is a team of analysts who monitor your environment 24/7, investigate those alerts and contain threats for you.
XDR, the third acronym in the pile, is another tool, one that pulls in data from more than your endpoints. Pick wrong and you land in one of two places: an EDR console full of alerts nobody reads at 2 a.m., or a contract for coverage your environment doesn’t need. Two questions keep you out of both.
Find out what you already own
What Is the Difference Between MDR and EDR?
EDR is a product you install. MDR is a service you hire. EDR detects suspicious activity on endpoints and gives you the controls to respond. MDR puts trained analysts behind those controls 24/7, so when a detection fires at 2 a.m., someone investigates and contains it that night instead of finding it in the queue on Monday.
What Does EDR Actually Do?
EDR runs an agent on each endpoint that records process launches, file changes, registry edits and network connections. It flags behavior that looks malicious and lets you isolate the host, kill the process or quarantine the file, often automatically. It hands you the evidence and the tools to investigate. It doesn’t supply the person who does the investigating.
Gartner’s market definition describes EDR tools as solutions that detect suspicious behavior, “block malicious activity, and provide remediation suggestions to restore affected systems”. Note the word suggestions. Recording behavior instead of matching signatures moved EDR past older tools, and it’s why the MDR vs traditional antivirus question rarely ends with antivirus winning.
What Does an MDR Provider Actually Do?
An MDR provider runs a remote security operations center (SOC) on your behalf. Its analysts watch your detection tools around the clock, triage alerts, hunt for threats the tools missed and take preapproved containment actions, such as isolating a host or disabling an account. A provider that only emails you a ticket is a monitoring service, not MDR.
Most IT leaders know roughly what MDR is. Vendors blur where the service ends and the tooling begins. Gartner defines MDR as services that “provide customers with remotely delivered security operations center (SOC) functions”, and its criteria call for 24/7 staffing and containment that goes “beyond alerting and notification”.
Speed is the point. According to IBM’s Cost of a Data Breach Report 2026, organizations took a mean of 247 days to identify and contain a breach, the first increase in five years. MDR runs on EDR telemetry and often adds Microsoft Entra ID sign-in logs, Microsoft 365 audit logs or a SIEM such as Microsoft Sentinel, with SOAR playbooks automating routine responses. The provider brings its own tools or operates yours.
Managed EDR is MDR with a narrower scope: the provider runs EDR on your endpoints but skips identity, email and cloud.
Where Does XDR Fit?
XDR (extended detection and response) is EDR’s bigger sibling: software that correlates signals from endpoints, identity, email, cloud and network tools in one console. It’s still a tool your team runs, not a service. XDR widens what you can see. It doesn’t add anyone to watch it.
Gartner calls XDR a “unified security incident detection and response platform that automatically collects and correlates data from multiple proprietary security components”, a definition CrowdStrike cites in its guide to XDR. Sophos puts it more plainly on its endpoint product page: its XDR “extends Sophos EDR with visibility across your entire attack surface”. Microsoft Defender XDR follows the same pattern, pulling Defender for Endpoint, Defender for Office 365, Defender for Identity and Defender for Cloud Apps into one incident queue. Identity threat detection and response (ITDR) sits inside that identity layer, though some vendors sell it separately.
The payoff is context. Picture an Entra ID sign-in from an unfamiliar country, an Exchange Online inbox rule that forwards invoices outside the company (catalogued in MITRE ATT&CK as Email Forwarding Rule, T1114.003) and a new PowerShell process on the same user’s laptop. Each looks minor in its own console. Correlated, they look like a compromised account.
Is XDR an Upgrade From MDR?
No. XDR and MDR answer different questions. XDR changes what you can see by adding identity, email, cloud and network data to endpoint telemetry. MDR changes who is watching by adding 24/7 analysts. You can run XDR with no MDR, buy MDR built on plain EDR, or combine the two.
One MSP’s comparison guide draws EDR at the center with “ITDR, MDR, and XDR as progressive rings” around it and tells complex environments they “will most likely need to level up to an XDR system”. An XDR console without analysts behind it is just a bigger screen with more alerts.
Microsoft adds to the confusion. It launched its own MDR service as Defender Experts for XDR, billed at the time as a managed extended detection and response (MXDR) service, and later renamed it. Its Defender Experts MDR documentation settles the question: “The service is the same; only the name changed”.
How Do You Tell Them Apart?
Ask two questions about any product. What does it cover: endpoints only, or endpoints plus identity, email, cloud and network? Who runs it: your team, or a provider’s analysts around the clock? Every option lands in one of four boxes.
EDR, XDR, Managed EDR and MDR at a Glance
| Option | What it is | What it covers | Who runs it | Best fit |
|---|---|---|---|---|
| EDR | Software (tool) | Endpoints: laptops, desktops, servers | Your team | Teams with someone who reviews and acts on alerts daily, including off-hours |
| XDR | Software (tool) | Endpoints plus identity, email, cloud, network | Your team | Teams with in-house security analysts who need cross-domain context |
| Managed EDR | Service | Endpoints | Provider's analysts, 24/7 | Lean IT teams whose main gap is endpoint coverage after hours |
| MDR | Service | Endpoints and usually more, depending on the provider | Provider's analysts, 24/7 | Lean IT teams with no security staff who need investigation and containment across the environment |
NIST draws the same line. According to the NIST Cybersecurity Framework 2.0, organizations should monitor computing hardware, software and runtime environments for potentially adverse events (DE.CM-09), correlate information from multiple sources (DE.AE-03) and contain incidents (RS.MI-01). EDR covers the first and XDR adds the second. The third needs someone with authority to act, and NIST’s own examples for it include letting a managed security service provider contain incidents on the organization’s behalf.
Is CrowdStrike, SentinelOne or Arctic Wolf an EDR or an MDR?
Most of the big names sell both: a tool you run yourself and a service where their analysts run it for you. The brand doesn’t tell you which one you’re buying. The product name does. CrowdStrike Falcon Insight XDR is a tool, for example, while Falcon Complete Next-Gen MDR is a service.
Tool or Service? Where Common Products Sit
| Vendor | Tool (EDR/XDR) | Service (managed EDR/MDR) |
|---|---|---|
| CrowdStrike | Falcon Insight XDR (EDR with native XDR) | Falcon Complete Next-Gen MDR |
| SentinelOne | Singularity Platform (EDR/XDR) | Wayfinder MDR Essentials, Wayfinder MDR Elite |
| Sophos | Sophos Endpoint (powered by Intercept X), Sophos EDR, Sophos XDR | Sophos MDR (includes Sophos XDR) |
| Arctic Wolf | Aurora Endpoint Defense | Arctic Wolf Managed Detection and Response; Aurora Managed Endpoint Defense |
| Huntress | None sold separately; Huntress bundles the agent with the service | Huntress Managed EDR (agent, platform and 24/7 SOC in one price) |
| Microsoft | Defender for Business, Defender for Endpoint Plan 1 and Plan 2, Defender XDR | Defender Experts MDR (formerly Defender Experts for XDR) |
Endpoint vendors (CrowdStrike, SentinelOne, Sophos, Microsoft) built the tool first and added a service on top. Huntress and Arctic Wolf lead with the service. Neither wins by default. What decides it is whether the service covers the data sources you care about and whether its analysts can act, not just notify.
Bring us your shortlist
Which One Does Your Team Actually Need?
If nobody on your team owns security alerts at night or on weekends, you need a service: MDR or managed EDR. If someone can watch and act on alerts every hour of every day, a tool may be enough.
When EDR on Its Own Is Enough
EDR alone works when a named person triages detections daily, writes exclusions for false positives, responds after hours and has a backup for vacation weeks. If the plan is “the help desk will keep an eye on it”, you’re buying a very good smoke detector and installing it in an empty building.
When You Need MDR
MDR makes sense when any of these are true:
- No one on staff has security as their primary job.
- Alerts that fire after 5 p.m. wait until morning.
- You already own EDR, but nobody has time to tune it, so alert fatigue has set in.
- Your insurer, auditors or customers ask who monitors your environment and how fast you respond.
Attackers don’t keep office hours. According to Verizon’s 2026 Data Breach Investigations Report, exploitation of software vulnerabilities was the initial access vector in 31% of breaches, overtaking stolen credentials for the first time in the report’s 19-year history. Patching closes those doors eventually. Detection catches whoever walked through first.
That’s the gap Meriplex managed detection and response fills, with 24/7 monitoring of your network and endpoints, AI-driven detection with automated responses, threat hunting, incident response, forensic analysis and analyst-led investigations.
The Co-Managed Middle Ground
If your team covers business hours well and nothing else, co-managed MDR splits the job. Your IT team runs the console by day, because they know which alerts are normal. The provider covers nights, weekends and holidays, and backs you up on serious incidents.
The handoff decides whether this works, so put two things in writing. First, an escalation matrix: who gets paged, in what order, and how incidents pass between teams at shift change. Second, a list of preapproved response actions, such as isolating a host, disabling an account or revoking active sessions, that the provider can take without calling first. Meriplex co-managed IT support splits the work along exactly those lines.
Check What You Already Own
Before you buy anything, check your Microsoft licensing. Microsoft 365 Business Premium includes Microsoft Defender for Business, which Microsoft says “delivers endpoint protection and EDR for your devices”. If you’re on Business Premium, you already own EDR, whether or not anyone has configured it.
There’s a catch for the mid-market. Microsoft’s Business Premium FAQ caps the Business plans at 300 seats in total. Above that, the EDR picture changes by plan, and Microsoft 365 E3 is a step down: its Defender for Endpoint Plan 1 covers prevention, not EDR. That’s easy to miss when a company outgrows Business Premium. Mixed tenants need care too: Microsoft’s Defender for Business FAQ notes that a tenant with both Defender for Business and Defender for Endpoint Plan 2 “defaults to the Defender for Business experience”.
Which Microsoft 365 Plans Include EDR?
| Plan | Defender product included | Full EDR? | Seat limit |
|---|---|---|---|
| Microsoft 365 Business Premium | Defender for Business | Yes | Up to 300 seats across all Business plans |
| Microsoft 365 E3 | Defender for Endpoint Plan 1 | No: prevention and manual response actions only | No Business-plan cap |
| Microsoft 365 E5 | Defender for Endpoint Plan 2 | Yes, with advanced hunting and automated investigation | No Business-plan cap |
When we review a Business Premium tenant, the first thing we open is the device inventory in the Microsoft Defender portal. The usual finding is a gap between what's licensed and what's protected. Some laptops were never onboarded, servers sit outside Defender entirely, and the incident queue holds weeks of medium-severity alerts with no owner. The fix starts with onboarding every device and assigning the queue, not with buying a new tool.
Owning the tool is step one. Someone still has to watch it at 2 a.m.
What Should You Ask Before Buying MDR?
Ask four things before you sign: what data the provider covers, whether it contains threats, whose EDR it runs, and how after-hours escalation works. The answers separate services that fit your environment from ones that only fit the sales deck.
- Which data sources are covered? Endpoints only, or also Entra ID sign-ins, Microsoft 365 audit logs, firewall logs and cloud workloads? Get the list in writing.
- Do they contain threats, or only notify you? Ask which actions analysts can take under preapproved runbooks, such as host isolation or account disablement, and which need your approval.
- Do you bring your own EDR or use theirs? Some operate the EDR you already run, including Microsoft Defender. Others require their own agent.
- How does after-hours escalation work? Who gets called, in what order, and what happens if nobody answers?
Pricing models and response tiers earned a post of their own, and our cost-vs-risk breakdown works through both.
Frequently Asked Questions
Do You Need EDR If You Have MDR?
Yes, but you usually don’t buy it separately. MDR needs endpoint telemetry, and EDR supplies it. Some providers bundle their own agent: Huntress Managed EDR includes the agent and a 24/7 SOC in one price. Some build on a specific stack, as Sophos MDR does with Sophos XDR. Others run the EDR you already own.
Do You Need EDR If You Have XDR?
No separate purchase is needed, because XDR includes EDR at its core. CrowdStrike describes Falcon Insight XDR as unifying “endpoint detection and response (EDR) with identity, cloud, and mobile telemetry”, and Sophos builds XDR as an extension of Sophos EDR. The endpoint agent still collects the raw data. XDR adds the context around it.
Does Cyber Insurance Require EDR or MDR?
Many insurers expect EDR. Fewer name MDR outright. Broker Marsh lists EDR among its 12 key cybersecurity controls, and its CISO’s guide to insurability says insurers expect EDR “as a minimum” across servers and laptops. Coalition lists antivirus or EDR software among its cyber insurance requirements.
An EDR console nobody watches is a weak answer to an after-hours monitoring question.
The Bottom Line
EDR and XDR are tools. Managed EDR and MDR are services. Separate what a product covers from who runs it, and vendor pitches get easy to decode. For most lean IT teams, the missing piece isn’t a tool. It’s hours: the nights and weekends when alerts fire and nobody answers.